Blogg V2
An async FastAPI blog hardened into a production app: httpOnly cookie JWT auth with CSRF protection, private S3 profile pictures via short lived presigned URLs, and a full Docker deployment.
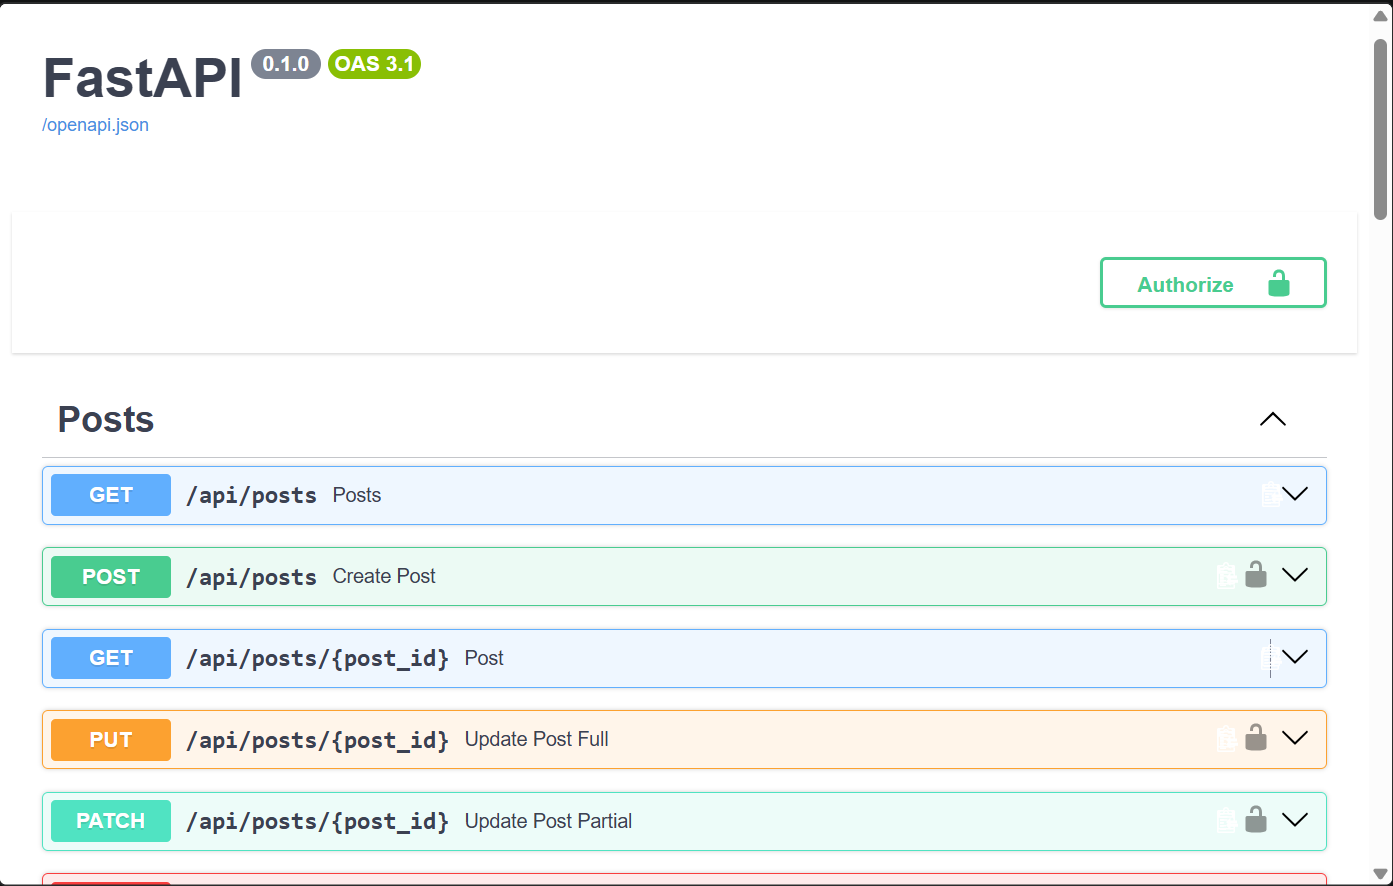
Overview
Started as a small blog and rebuilt as something deployable: async SQLAlchemy and Alembic on PostgreSQL, secure cookie auth, avatars stored in S3 that never go public, rate limited auth endpoints, and CI that runs lint, tests and image builds.
Key features
- Cookie JWT + CSRFhttpOnly
SameSite=Laxcookie plus a custom header CSRF check. - Private avatarsS3 objects stay private; served through short lived presigned URLs.
- Async data layerSQLAlchemy 2 async + Alembic migrations on PostgreSQL 17.
- Abuse controlsIn memory sliding window ratelimit on login and password reset.
- Docker deployApp container runs as a non root user,
alembic upgrade headon start, healthchecks. - CI to GHCRGitHub Actions: lint + pytest on Postgres service, then image push on main.
Endpoints
| Method | Path |
|---|---|
| POST | /api/users (register) |
| POST | /api/users/token (login, sets cookie) |
| GET | /api/users/me (current user) |
| PATCH | /api/users/{id}/picture (avatar upload) |
| GET | /api/posts?skip=0&limit=10 (paginated list) |
| GET | /health (readiness, checks Postgres) |
alembic upgrade head
uvicorn app.main:app --reload # http://127.0.0.1:8000
docker compose up -d --build # db + app, deploys like prod
Stack
Python 3.13
FastAPI
PostgreSQL
SQLAlchemy
Alembic
S3
Docker
Architecture notes
One uvicorn worker runs per container, with production sitting behind a TLS proxy
using COOKIE_SECURE=true, a real SECRET_KEY and
ALLOWED_HOSTS.